URL Fuzzer &Directory DiscoveryScanner
Continuous offensive security and exposure management for web applications, networks, APIs, and cloud infrastructure.
12M+
Paths tested daily
800+
Curated wordlists
99.1%
Uptime SLA
< 2s
Avg. first hit
50K+
Security teams
SOC 2 II
Certified
Find hidden directories and files instantly
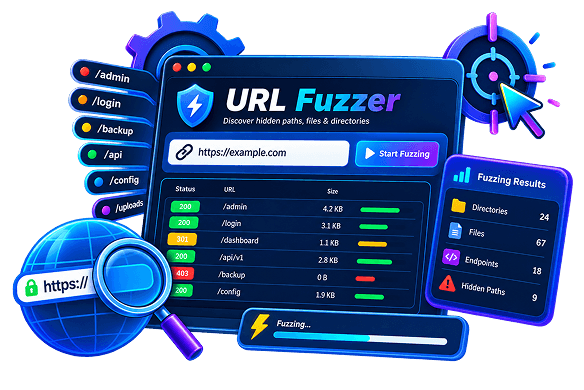
Blast thousands of common path patterns against any web server. Uncover admin panels, backup files, configuration endpoints, and sensitive data directories that aren't linked anywhere on the site.
Find hidden paths and endpoints with
documented evidence
Our fuzzer doesn't just list paths it captures the full HTTP response, annotates the risk level, and presents each discovery with complete evidence so your team can act immediately.
Every attack surface, fully fuzzed
Our scanner probes every dimension of your web infrastructure using purpose-built wordlists for each attack category.
Directory Bruteforce
Enumerate hidden directories using 4,000+ common path patterns across all popular frameworks.
Parameter Fuzzing
Discover undocumented GET/POST parameters, debug flags, and hidden API fields.
Virtual Host Discovery
Find hidden subdomains and VHosts co-located on the same IP address.
Extension Scanning
Test every path with .bak, .old, .sql, .zip, .log, .conf and 80+ more extensions.
Backup File Detection
Locate exposed database dumps, code backups, and archive files left on public paths.
API Endpoint Discovery
Surface undocumented REST and GraphQL endpoints using API-specific wordlists.
Admin Panel Detection
Identify admin, management, and CMS login interfaces across all popular platforms.
Config File Exposure
Detect exposed .env, .htaccess, web.config, and application configuration files.
Status code validation
Every discovered path is verified with a real HTTP request. We strip 404-like responses that return 200, using content-length and body hashing to eliminate false positives.
Response size filtering
Filter results by response body size to instantly distinguish real content from generic error pages served with wrong status codes.
Zero false positives
Our engine compares each response against a baseline fingerprint of the target's 404 page so your result list contains only genuine, reachable endpoints.
Trust Your Results.
Validate Every Path
Every finding goes through automated false-positive elimination before it surfaces. If a path is in your results, it's real confirmed with a live request, full response, and size validation.
See it in actionSample URL
Fuzzer
Discovery
Report
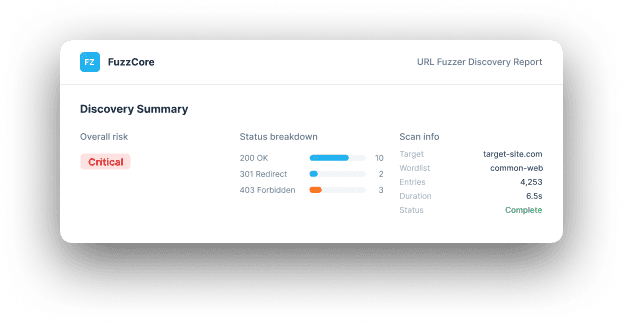
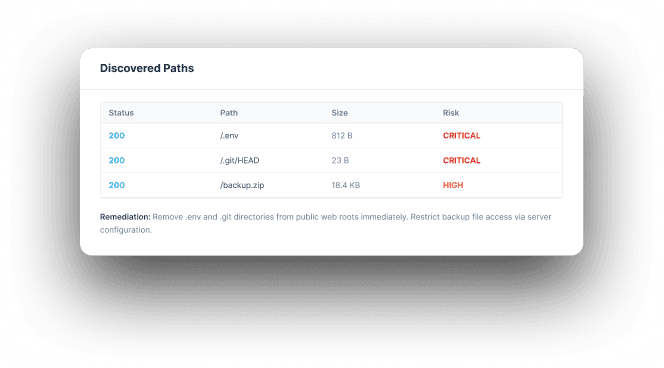
This sample report shows what you receive after every fuzz run the discovered paths, evidence, risk classification, and remediation guidance.
Download sample reportAn at-a-glance summary of the fuzz run total paths tested, hit rate, status code breakdown, and top risks discovered.
From fuzz to fix fully automated
Configure Target
Enter your URL, select a wordlist, set threads and timeout. Done in under 30 seconds.
Load Wordlist
Choose from 800+ curated wordlists or upload your own. Filtered for relevance to your stack.
Fuzz & Discover
Parallel fuzzing engine fires through every entry, capturing full HTTP responses in real time.
Filter & Analyse
Results auto-filtered for false positives. Grouped by status code, risk level, and response size.
Export Report
One-click export to PDF, JSON, CSV. Push directly to Jira, Linear, or your SIEM.
Use this tool from your command line interface
If you prefer it, we also provide a CLI version of our Website Vulnerability Scanner. Through the ScanCore CLI, you can run scans against your web apps and start gathering insights for your next move.
1. Installation
If you have docker or pip installed, you can use them to get scancore:
2. Usage
Quickstart: run the following command in your terminal to find the vulnerabilities of your website.
You can learn more options with the --help flag:
Frequently asked questions
Everything you need to know before your first scan.
Yes, the URL fuzzer is designed to be safe for production environments. You can throttle request rates and set concurrent thread limits to ensure no disruption to your services.