Audit-Ready Internal Security
Internal vulnerability scanning for audit-ready evidence
Scan internal systems straight from the cloud and skip the complexity of deploying or maintaining on-premise appliances. Prove which threats behind your firewall are actually exploitable, move beyond raw CVE lists and turn findings into defensible, audit-ready evidence for frameworks like SOC 2 and ISO 27001.
Compare pricing plans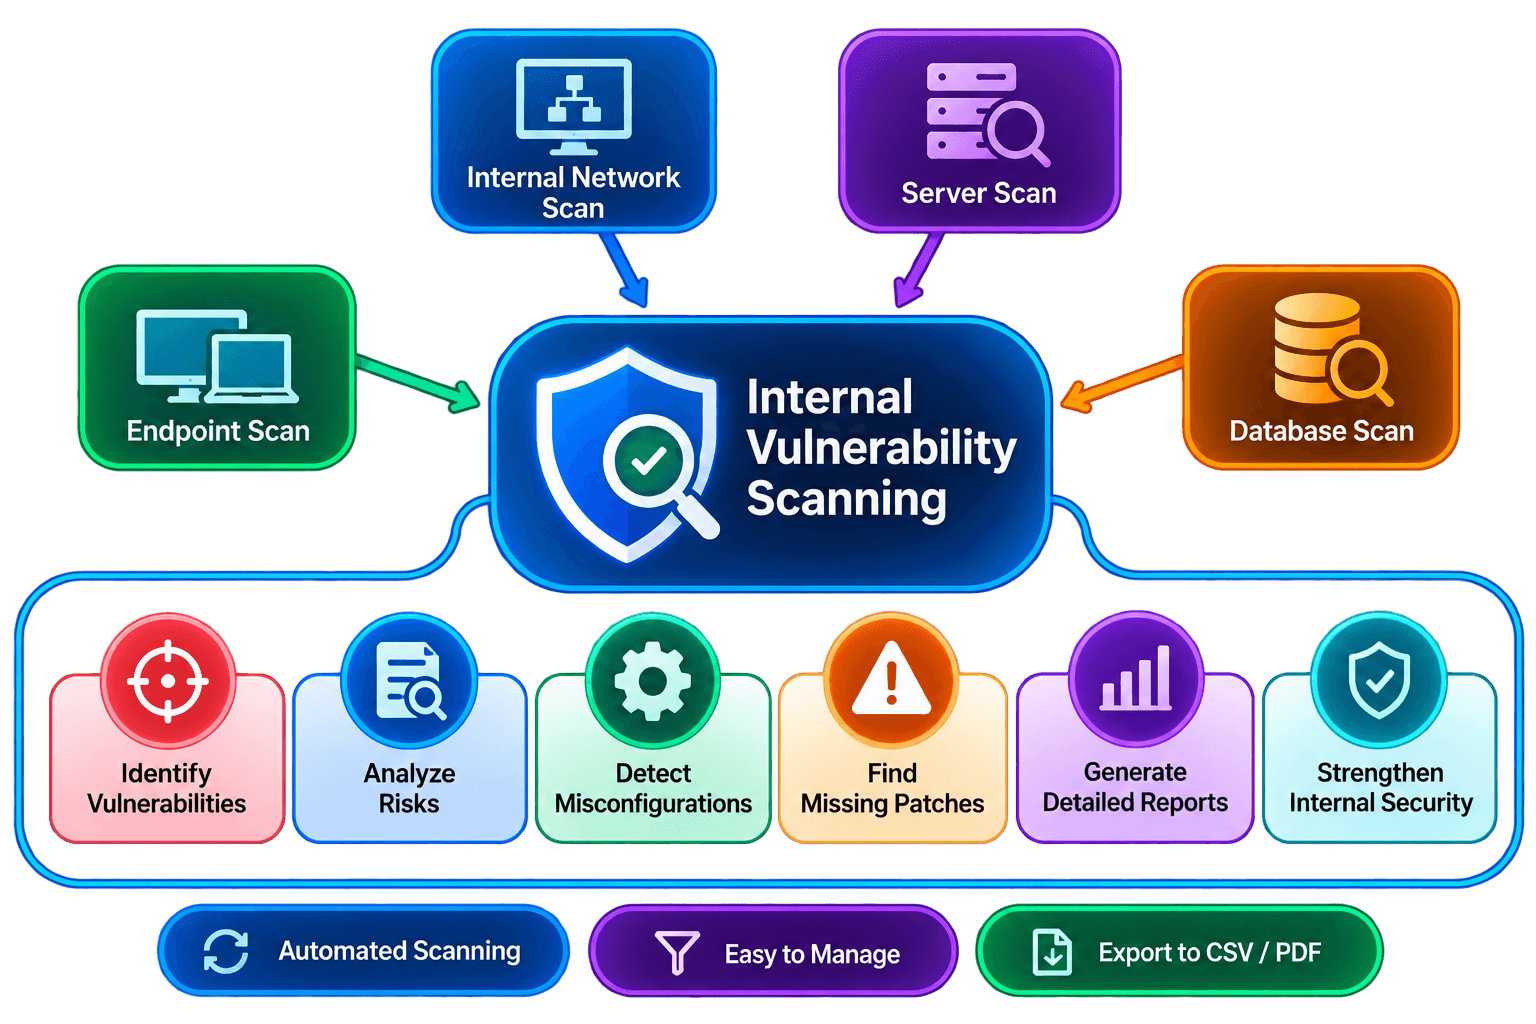
Internal Security
Why raw internal scans fail compliance audits
Most security programs focus on preventing external access, but once an attacker gets inside, internal systems determine the real impact. For security and compliance teams, simple detection is just the starting point, because auditors don't just ask if you ran a scan.
Unvalidated findings lack proof
Simply generating a list of internal CVEs leaves the burden of proof on your team. Auditors routinely reject raw output unless you can explicitly demonstrate that a vulnerability is exploitable and provide verifiable evidence, like screenshots or request traces, that prove it exists in your specific environment.
Lack of retest proof
Auditors demand proof that you have closed the security gaps behind your firewall. You need to show not just what was found, but that it was successfully resolved. A before-and-after differential report lets you show the exact same scan profile after remediating, so you can satisfy auditors with clear, reproducible proof.
Manual rework bottlenecks
Without reproducible evidence, teams are forced into manual rework: capturing screenshots of internal states, validating exploitability on private IPs, and recompiling reports by hand.
Internal Security
How to run internal scans for compliance with CyberScan
Deploy and schedule
Connect your cloud scanners to your internal network via the VPN Agent or your own custom OpenVPN setup. Schedule scans against internal IP ranges to identify unpatched services, weak credentials, and misconfigurations that enable lateral movement.
Validate and prove
Don't just list CVEs - confirm them. Use automated validation features to safely prove high-risk findings are exploitable in your specific environment. Automatically capture evidence like screenshots and request/response traces, and use a Password Auditor to confirm weak passwords.
Remediate and re-test
Once fixes are applied, re-run the exact same scan profile. This automatically generates a ‘before-and-after’ differential record that clearly highlights resolved vulnerabilities.
Export audit-ready evidence
Export validated findings mapped directly to your compliance controls and prove it. Turn internal scanning into a continuous, evidence-backed process.
Quick Deployment
See it in action - start internal scanning in minutes
Deploying an internal scan shouldn't require a complex network reconfiguration or heavy appliances. Watch how to securely link our cloud-based scanners to your private network using the VPN Agent.
Internal Assessment
How to perform an internal vuln. assessment
Full-Powered Toolkit
Internal vulnerability scanning tools
When assessing systems inside your network, you need the exact same rigor you apply to your perimeter. CyberScan's tools don't use a separate, limited toolset for internal assessments. You use our standard, full-powered tools, securely routed to your private IP range via the VPN Agent or your OpenVPN server. This guarantees consistent results and reproducible evidence for your compliance audits.
Network Vulnerability Scanner
Run secure, deep scans inside your private infrastructure to detect hosts, open ports, and missing security patches.
Password Auditor
Audit password security to proactively find weak or reused credentials across your internal network.
Website Vulnerability Scanner
Scan and fingerprint web apps that often go untested because they aren't public-facing.
Sniper: Auto-Exploiter
Safely validate high-risk findings with automated exploits to capture reproducible proof (like screenshots and request/response traces) that satisfies auditors.
Pentest Robots
Automate repetitive testing flows to maintain continuous visibility over your internal attack surface.
Customer Stories
How customers use CyberScan for web app pentesting
Overall a great tool for pentesting
The tool covers a lot of ground in one place. We use it to speed up the repetitive parts of our assessments and to deliver cleaner reports to our clients. It has become part of our standard workflow.
Alex Morgan - Security Consultant
Review source placeholder
Frequently asked questions
Everything you need to know before your first scan.
Yes. Scans are non-destructive and rate-limited by default, and any payload that could have side effects runs through sandboxed proof-of-concept validation instead of against your live system, so normal traffic and uptime are unaffected.