CloudVulnerabilityScanner
Continuous offensive security and exposure management for web applications, networks, APIs, and cloud infrastructure.
47,000+
Security professionals
2.1B+
Vulnerabilities found
99.3%
Detection accuracy
< 0.8%
False positive rate
1,200+
Pentest firms
SOC 2 II
Certified & ISO 27001
Discover Your Cloud Attack Surface
Identify internet-facing assets, exposed services, and potential entry points across your cloud-connected infrastructure. Build a clearer picture of your external attack surface and understand where unnecessary exposure may create security risks.
Use discovered assets and prioritized findings to investigate potential weaknesses and focus remediation efforts on the areas that matter most.
Identify risks across your cloud infrastructure
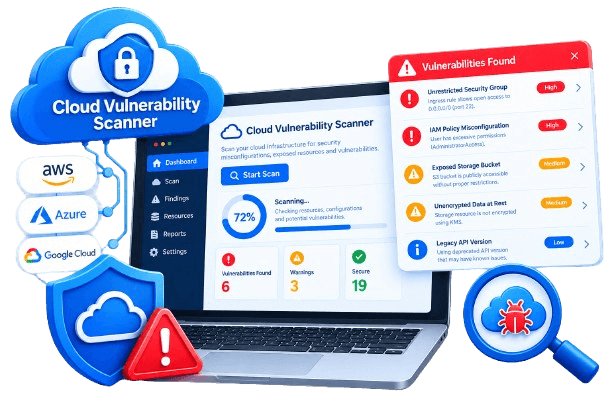
Assess cloud configurations, access permissions, exposed resources, and security controls to identify potential weaknesses and prioritize remediation.
Identity & Access Management
Identify overly permissive access policies, excessive privileges, and potentially risky identity configurations in supported cloud environments.
Cloud Misconfigurations
Review supported cloud resource settings for common security weaknesses, unsafe configurations, and unnecessary exposure.
Storage Security
Identify potentially public storage resources and access settings that could expose sensitive data to unintended users.
Network Exposure
Review supported network rules, firewall settings, and externally reachable services for unnecessary access.
Data Encryption
Check supported resources for encryption configuration gaps that may weaken the protection of stored or transmitted data.
Logging & Monitoring
Identify missing or incomplete logging and monitoring configurations that may limit security visibility and incident investigation.
Public Resource Exposure
Find cloud resources that may be accessible from the internet beyond their intended exposure and access requirements.
Compliance Posture
Review relevant configuration findings against supported security benchmarks to help identify potential compliance gaps.
Cloud Security Findings & Remediation
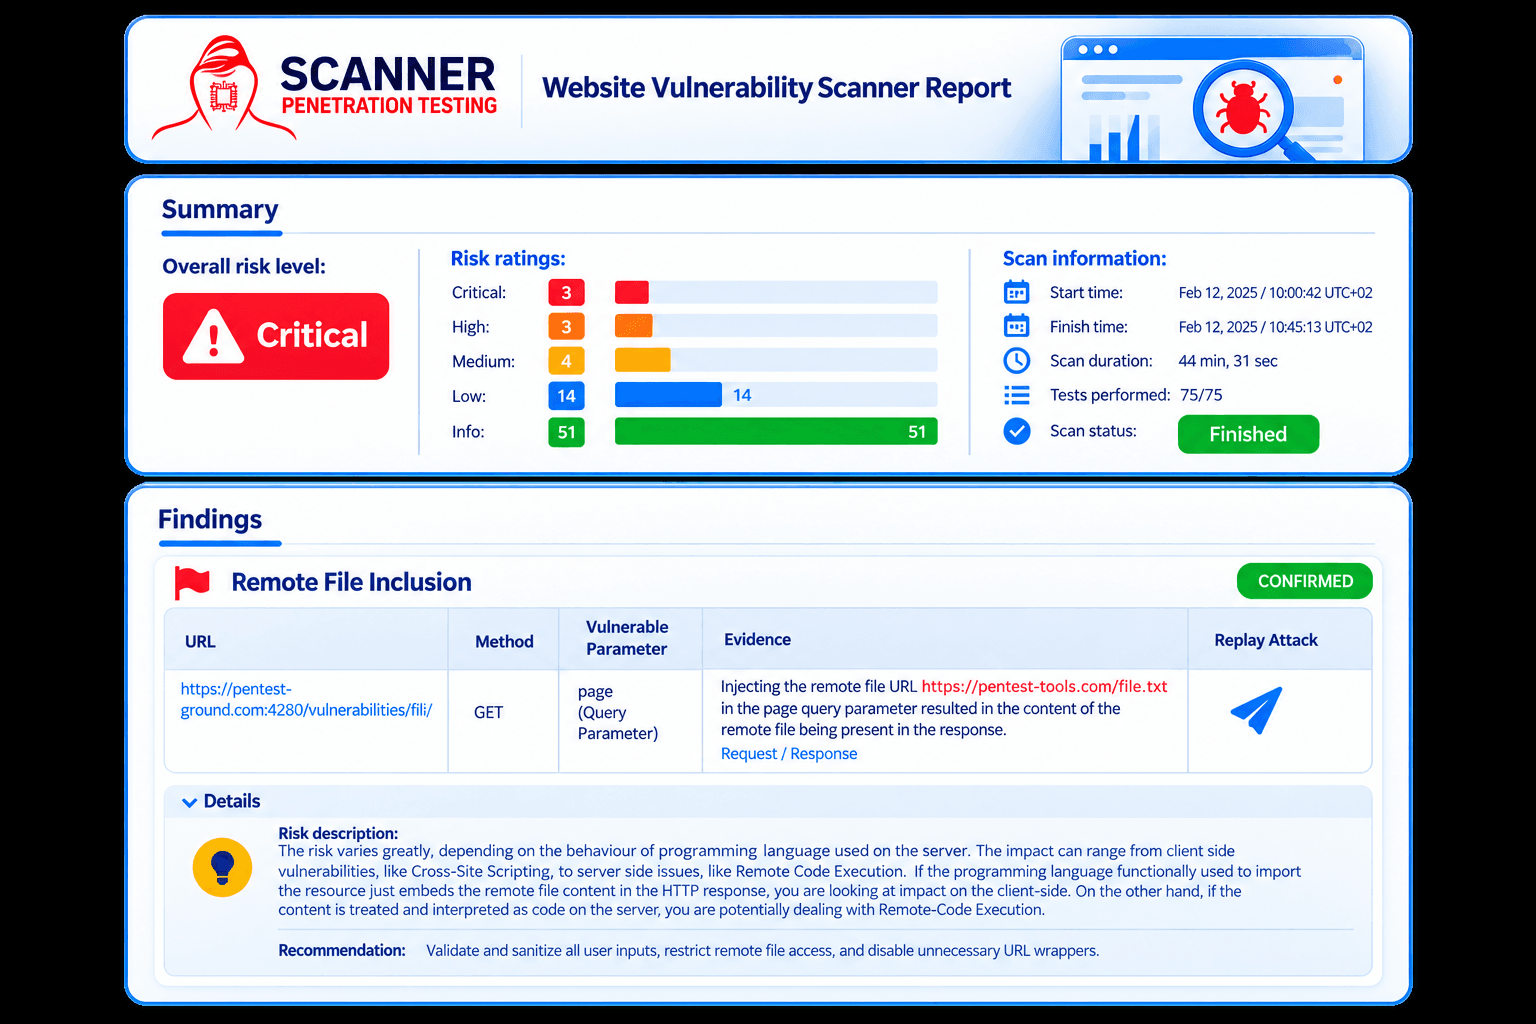
Turn cloud security findings into actionable improvements. Understand potential risks, review available evidence, and prioritize remediation to help reduce unnecessary exposure across your cloud environment.
Configuration Risk Analysis
Understand how cloud configuration weaknesses can increase exposure and create potential security risks.
Detailed Security Findings
Review available resource details, configuration evidence, and finding context to support security investigations.
Actionable Remediation
Use practical remediation guidance to address identified weaknesses and improve your cloud security posture.
From scan to fix fully automated
Wire vulnerability discovery directly into your development pipelines. No manual triage handoffs.
Scan & Discover
Auto asset discovery and vulnerability scanning triggers on schedule, code push, or deployment webhook.
AI Triage
The AI engine validates, deduplicates and ranks findings. Only confirmed issues reach your team.
Prioritize & Assign
Risk-ranked findings route to the right team automatically via Jira, Linear, or Slack with full context.
Remediate & Verify
Developers fix guided by AI-generated patches. Automated re-scan confirms the fix is clean.
Report & Prove
One-click reports for executives, clients, and auditors customized, white-labeled, always current.
Frequently asked questions
Everything you need to know before your first scan.
Yes. Scans are non-destructive and rate-limited by default, and any payload that could have side effects runs through sandboxed proof-of-concept validation instead of against your live system, so normal traffic and uptime are unaffected.