ApiVulnerabilityScanner
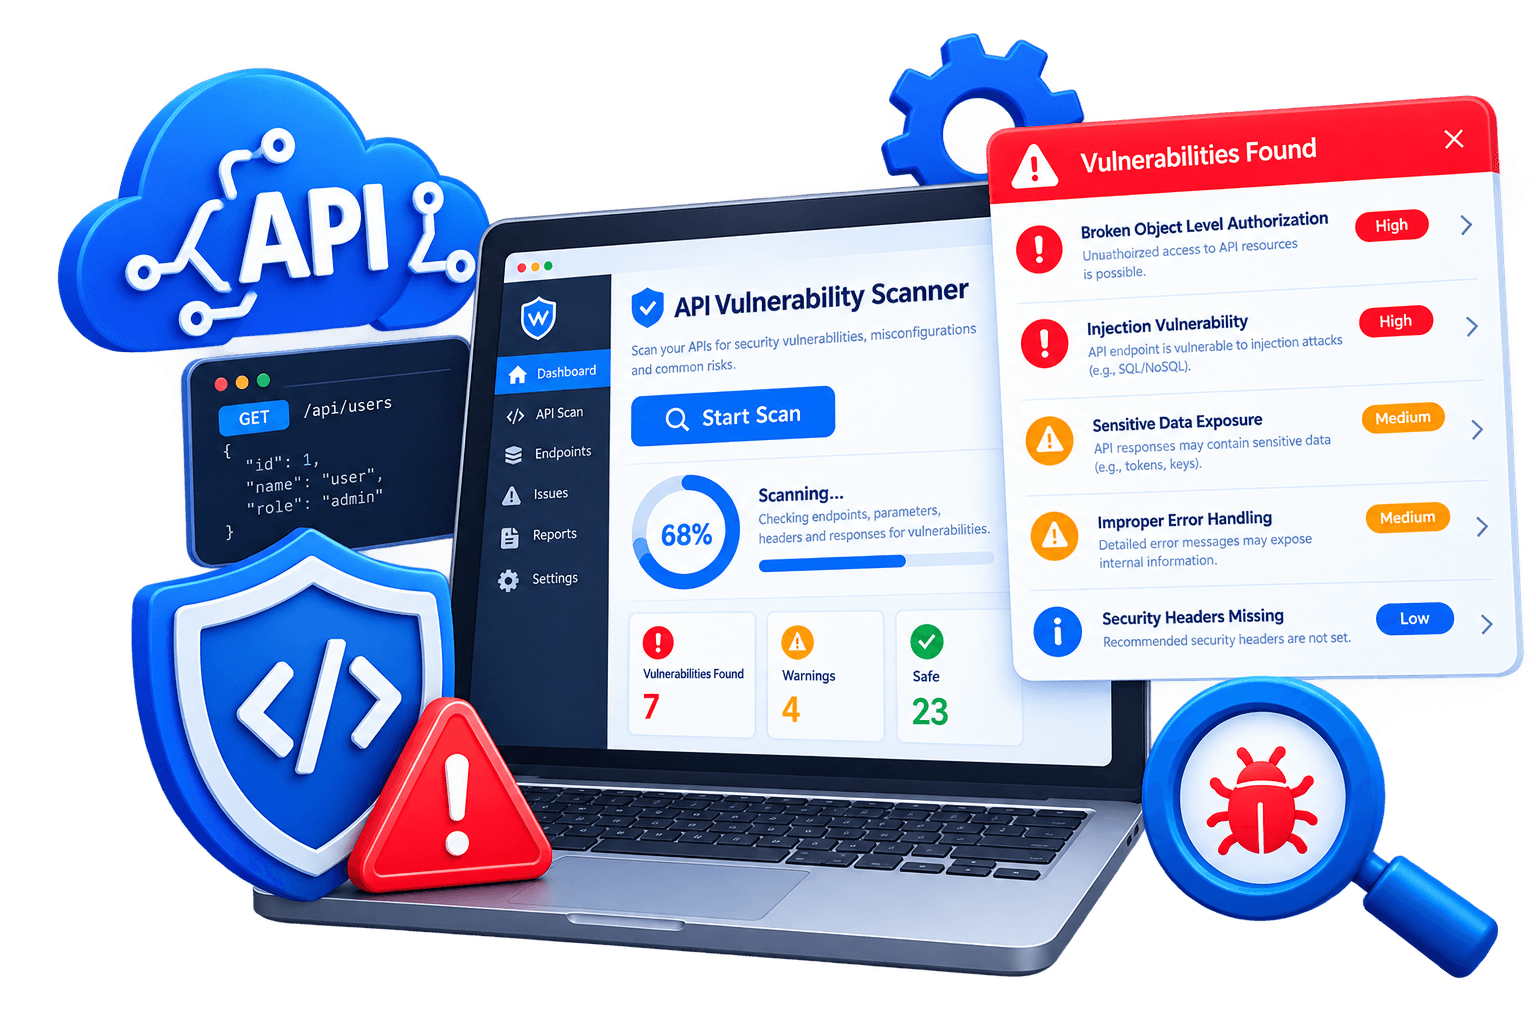
Continuous offensive security and exposure management for web applications, networks, APIs, and cloud infrastructure.
47,000+
Security professionals
2.1B+
Vulnerabilities found
99.3%
Detection accuracy
< 0.8%
False positive rate
1,200+
Pentest firms
SOC 2 II
Certified & ISO 27001
A supercharged Network Scanner for your Infrastructure
It combines multiple engines and fine-tuned (customizable) scan settings which surface critical vulnerabilities, misconfigurations, and outdated services. Each scan automatically updates your attack surface and provides an up-to-date map for planning targeted attacks or strategic lateral movements.
Purpose-built testing for every API attack
Our scanner runs 16+ checks across every layer of your web stack, returning verified, prioritised findings with fix guidance.
Object Authorization
Certificate validity, cipher strength, TLS version support, HSTS preload status.
Authentication
HSTS, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy.
API Injection
Presence, policy strictness, unsafe-inline detection, nonce/hash usage.
Data Exposure
Origin wildcards, preflight handling, credentials exposure on cross-origin requests.
Rate Limiting
Secure, HttpOnly, SameSite flags across all session and authentication cookies.
Server-Side Requests
Server version leaks, framework exposure, debug headers, error page information.
GraphQL Security
X-XSS-Protection header, CSP script-src policy, injection point detection.
Shadow APIs
HTTP to HTTPS redirect chain, redirect target validation, mixed-content detection.
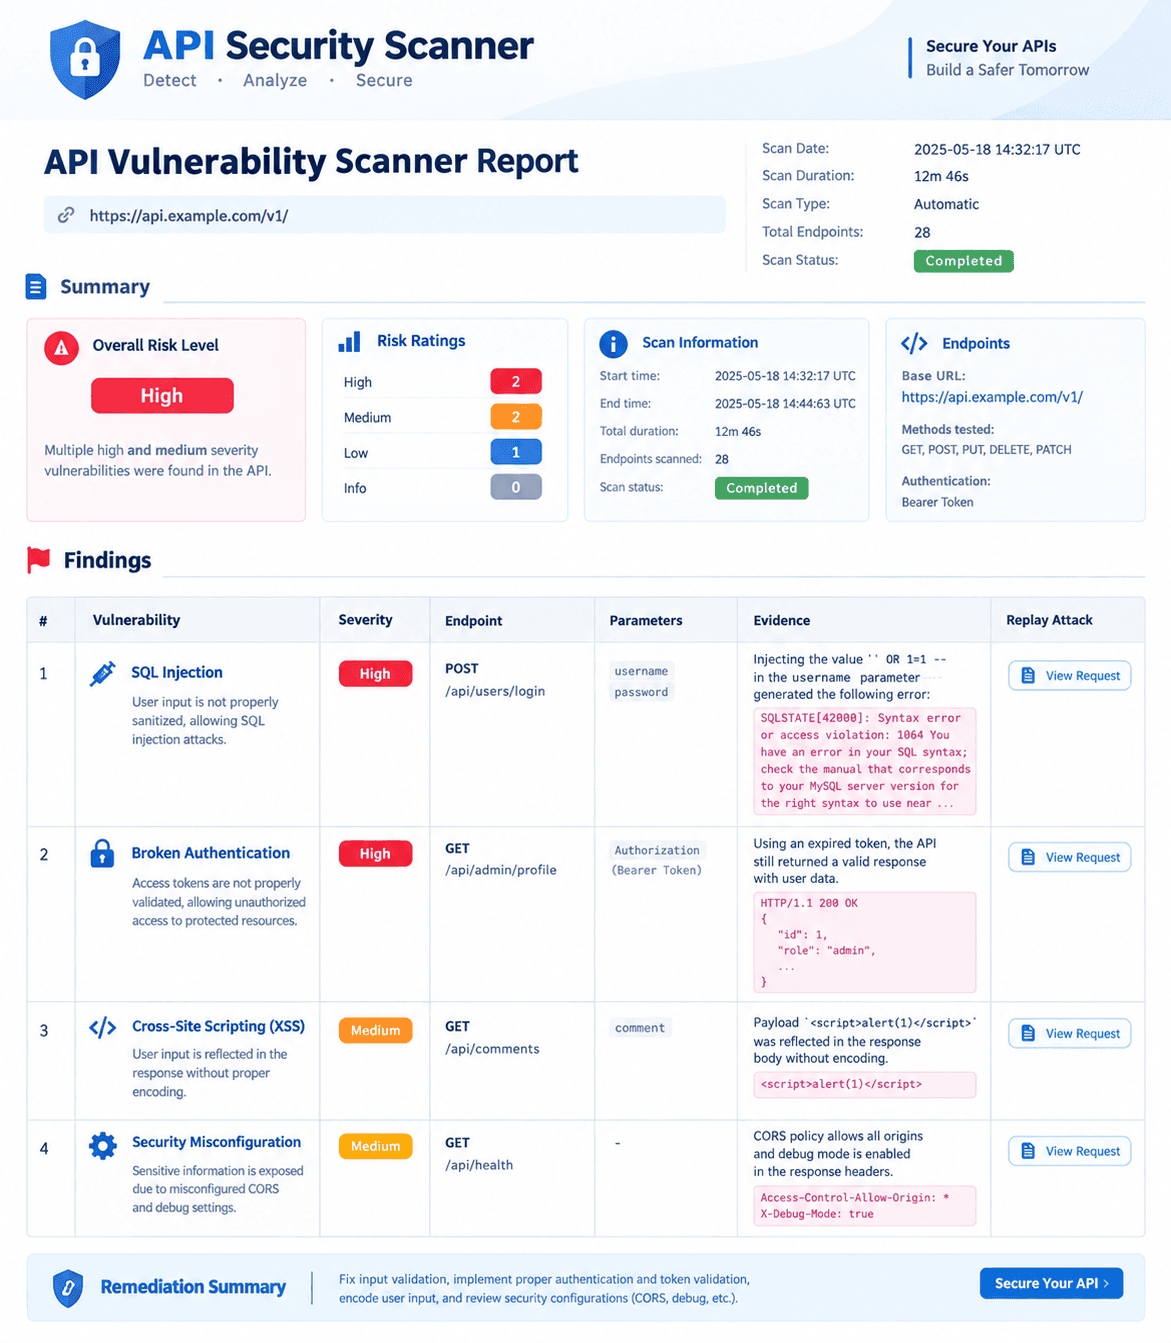
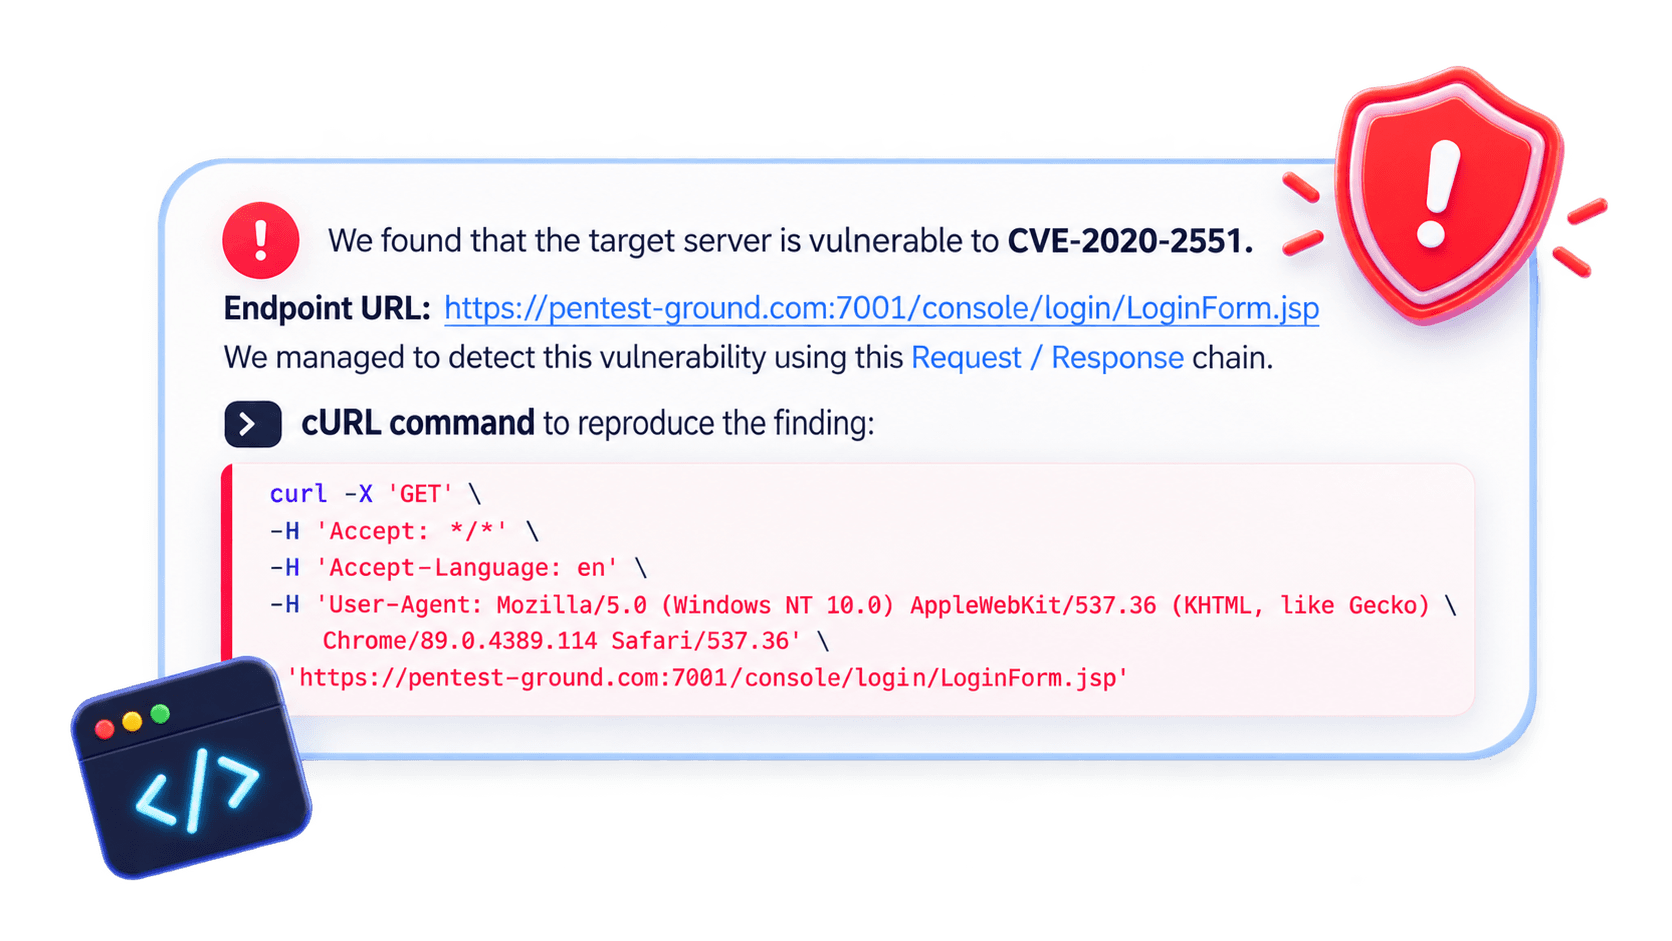
Sample API Vulnerability Scanner Report
Every critical finding goes through sandboxed PoC execution before it alerts. If it can't be confirmed exploitable, it doesn't surface.
Sandboxed execution
Payloads run in full isolation — zero risk to your production environment.
Evidence capture
PCAP captures, HTTP transcripts, and timing proofs attached to every finding.
Sub-1% false positives
Industry-leading signal quality. Your team reviews real risk, not noise.
From scan to fix fully automated
Wire vulnerability discovery directly into your development pipelines. No manual triage handoffs.
Scan & Discover
Auto asset discovery and vulnerability scanning triggers on schedule, code push, or deployment webhook.
AI Triage
The AI engine validates, deduplicates and ranks findings. Only confirmed issues reach your team.
Prioritize & Assign
Risk-ranked findings route to the right team automatically via Jira, Linear, or Slack with full context.
Remediate & Verify
Developers fix guided by AI-generated patches. Automated re-scan confirms the fix is clean.
Report & Prove
One-click reports for executives, clients, and auditors customized, white-labeled, always current.
Frequently asked questions
Everything you need to know before your first scan.
Yes. Scans are non-destructive and rate-limited by default, and any payload that could have side effects runs through sandboxed proof-of-concept validation instead of against your live system, so normal traffic and uptime are unaffected.